GDPR and EU MDR Compliance via CMDB for Paris Pharmaceutical Manufacturers Still Starts With System Inventory

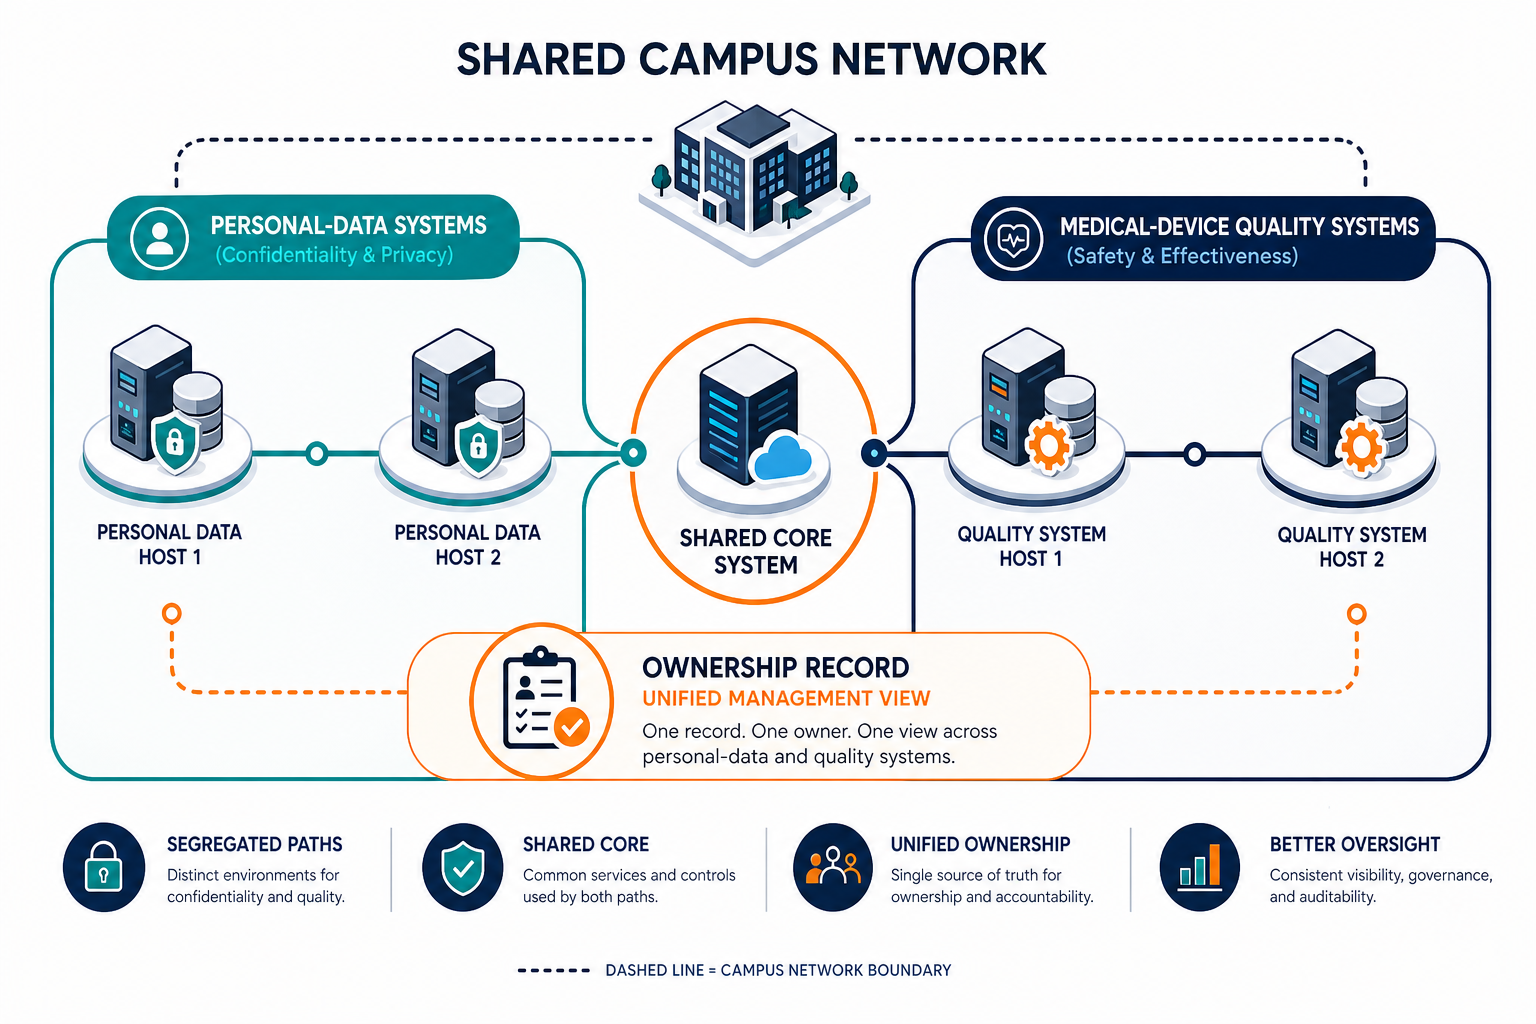
The quality and privacy sample in the Paris manufacturing campus did not open on a policy binder. It opened on three hosts that process trial subject data, hold device-related manufacturing records, or sit under a validated production path, then a simple ask: which systems store personal data, which systems sit inside the medical-device quality system, who owns each host today, and when that picture was last refreshed from discovery rather than a quarterly spreadsheet.
That is the real test of GDPR and EU MDR compliance via CMDB for Paris pharmaceutical manufacturers. French and EU privacy law and medical-device quality duties land on the same estate. Spreadsheet inventories that look complete in a workshop still fail when the sample hits a shared lab network, a contractor imaging station, a cloud SaaS path, or a validated host that never sat in the CMDB with a dated last-seen.
This page is not a full GDPR how-to for every database class. For database-layer auditor findings, use How to Ensure GDPR Compliance for Databases and Avoid Auditor Findings. It is also not a generic CMDB primer. Here the lens stays on Paris pharmaceutical manufacturers that must defend both personal-data processing and medical-device quality system integrity with one infrastructure evidence layer.
For the category frame before you rewrite another inventory policy, start with Trusted Runtime Truth.
Why dual-regime samples fail Paris pharma estates differently than a single privacy workshop
Paris-area pharmaceutical manufacturers often run clinical, commercial, and device-adjacent manufacturing paths on shared campuses. GDPR duties cover personal data processing and security of processing. EU Medical Device Regulation (EU MDR) duties cover quality management, technical documentation, and post-market surveillance for devices placed on the Union market. The systems that support both regimes often share the same network fabric, identity plane, and contractor jump boxes.
| Dual-regime failure | What the sample often finds | Why Paris pharma hits it first |
|---|---|---|
| Unowned personal-data hosts | Trial or HR systems with no CI owner | Privacy and ITAM lists diverge |
| Validated path without CMDB join | GxP host missing from live inventory | Quality system and IT estate disagree |
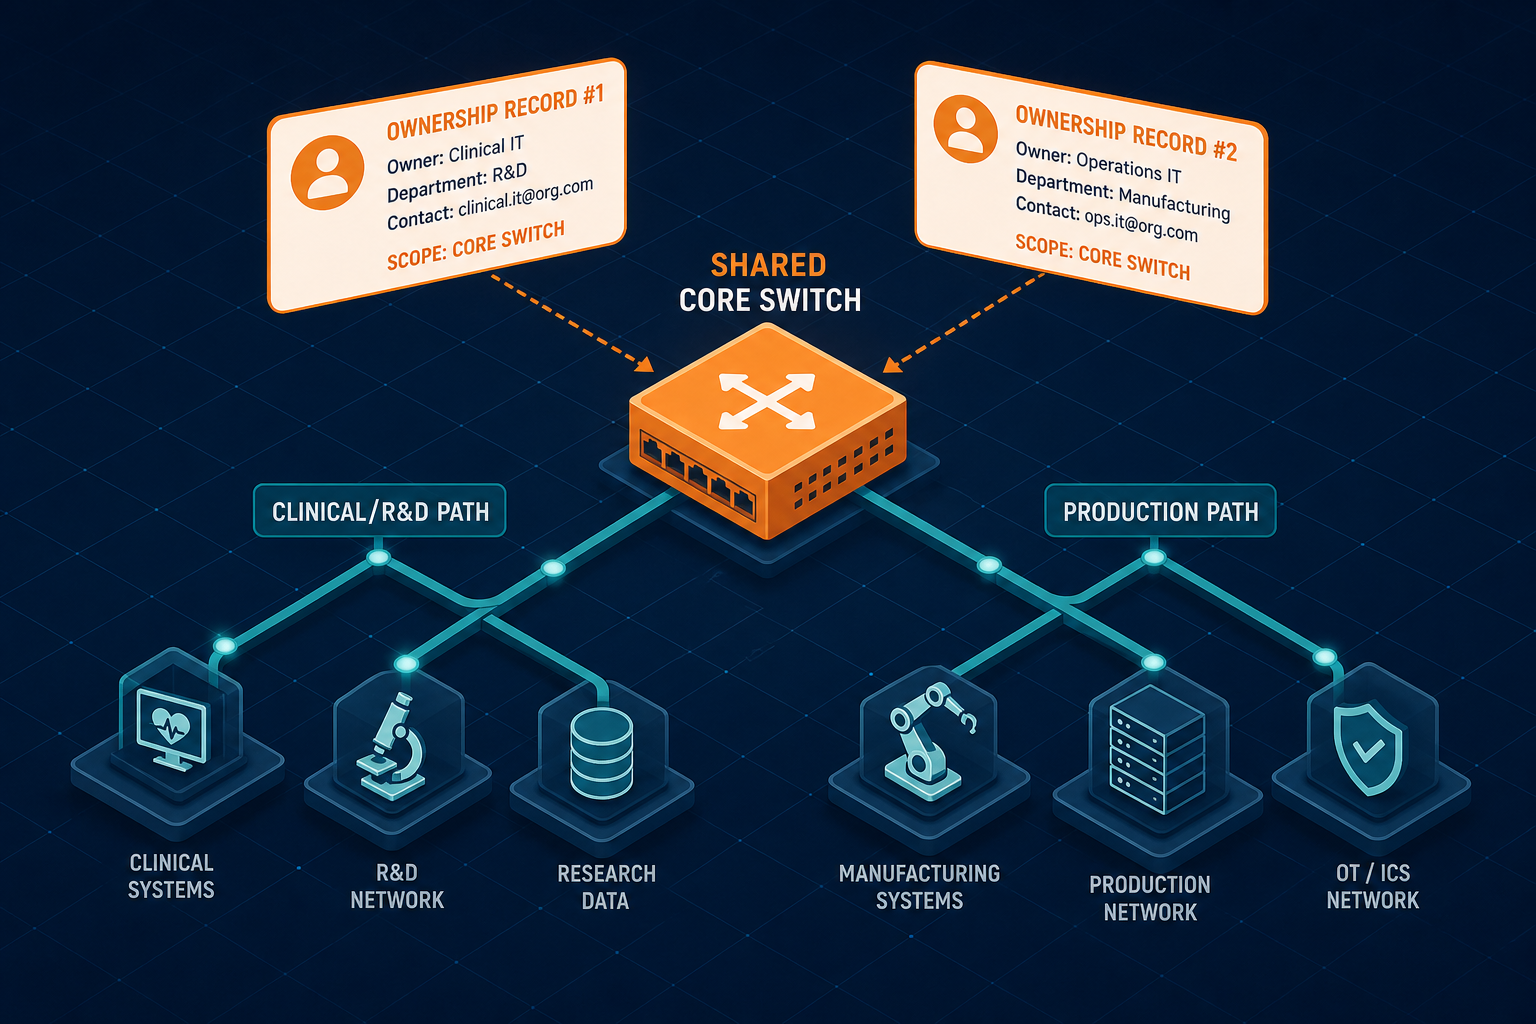
| Shared lab and plant fabric | Core switch under both R&D and production | One hop, two risk registers |
| Contractor and CRO gear | Imaging stations outside either CMDB | Vendors refresh without tickets |
| Cloud and SaaS control planes | Subscriptions with no service join | Clinical and QMS SaaS expand faster than imports |
| Stale last-seen on change samples | Decommissioned host still in production | Campus projects outrun quarterly cleanups |
The European Commission data protection overview frames GDPR as the Union privacy framework. gdpr.eu restates core principles in plain language. On the device side, the Commission medical devices new regulations page and the EMA medical devices overview describe the MDR and related device rules. French market surveillance still sits with ANSM, and privacy supervision with the CNIL. None of those authorities treat an undated spreadsheet as proof that system inventory holds under sampling.
CISA Binding Operational Directive 23-01 is a U.S. federal inventory rule, not EU law. Enterprise programs still use the same operational lesson: incomplete asset inventories break every control that claims coverage.
What GDPR and EU MDR compliance via CMDB means here
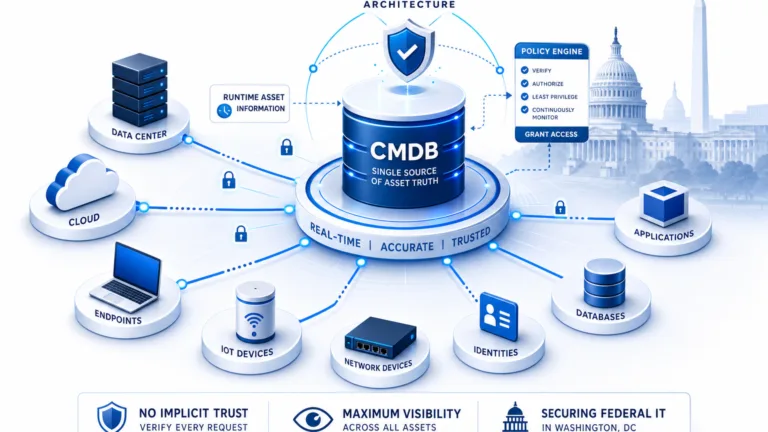
GDPR and EU MDR compliance via CMDB for Paris pharmaceutical manufacturers is the infrastructure evidence layer that records of processing, security of processing, change control, and device quality system integrity all lean on when auditors sample hosts, owners, and last-seen dates. Concretely, it means a dated, owned overview of the IT systems and dependencies that support personal-data processing and medical-device quality or manufacturing paths in scope. That overview only counts when it is refreshed from discovery-sourced records rather than one-off workshops.
It is not:
- A substitute for CNIL filings, DPO advice, or French transposition counsel
- A full QMS, eQMS, or Notified Body technical file product
- A claim that Virima is a GRC, clinical trial, or pharmacovigilance platform
- Automatic invention of GxP validation status without quality-system inputs
What does dual-regime CMDB compliance mean for Paris pharma manufacturers?
It is a discovery-sourced, owned inventory of systems and dependencies that support personal-data processing and medical-device quality or manufacturing paths on Paris pharma estates. Auditors sample hosts, owners, freshness dates, and service joins. Policy binders without that evidence fail the same controls they claim to meet.
Six inventory gaps that break dual-regime samples
1. Personal-data systems without a single accountable CI owner
Trial, HR, CRM, and support systems can process personal data while ITAM and privacy lists disagree on owner and location. GDPR accountability and security of processing need a defensible system list. Discovery that only populates hardware without owner fields leaves the governance gap open.
2. Validated and GxP-adjacent hosts missing from the live CMDB
EU MDR quality system inventory depends on knowing which systems sit under design, manufacturing, and post-market paths. The resource management duty in Article 10(9) assumes someone can name those systems. When validated hosts live only in a quality spreadsheet, change samples and CAPA reviews inherit a blind spot. The CMDB must carry identity and last-seen even when validation status stays in the QMS.
3. Shared campus fabric under both R&D and production
A core switch can sit under a clinical analytics path and a device manufacturing path and still have three owners in three tools. Dual-regime accountability needs one accountable role per relevant asset, not two incomplete lists.
4. CRO, CMO, and contractor gear treated as someone else’s problem
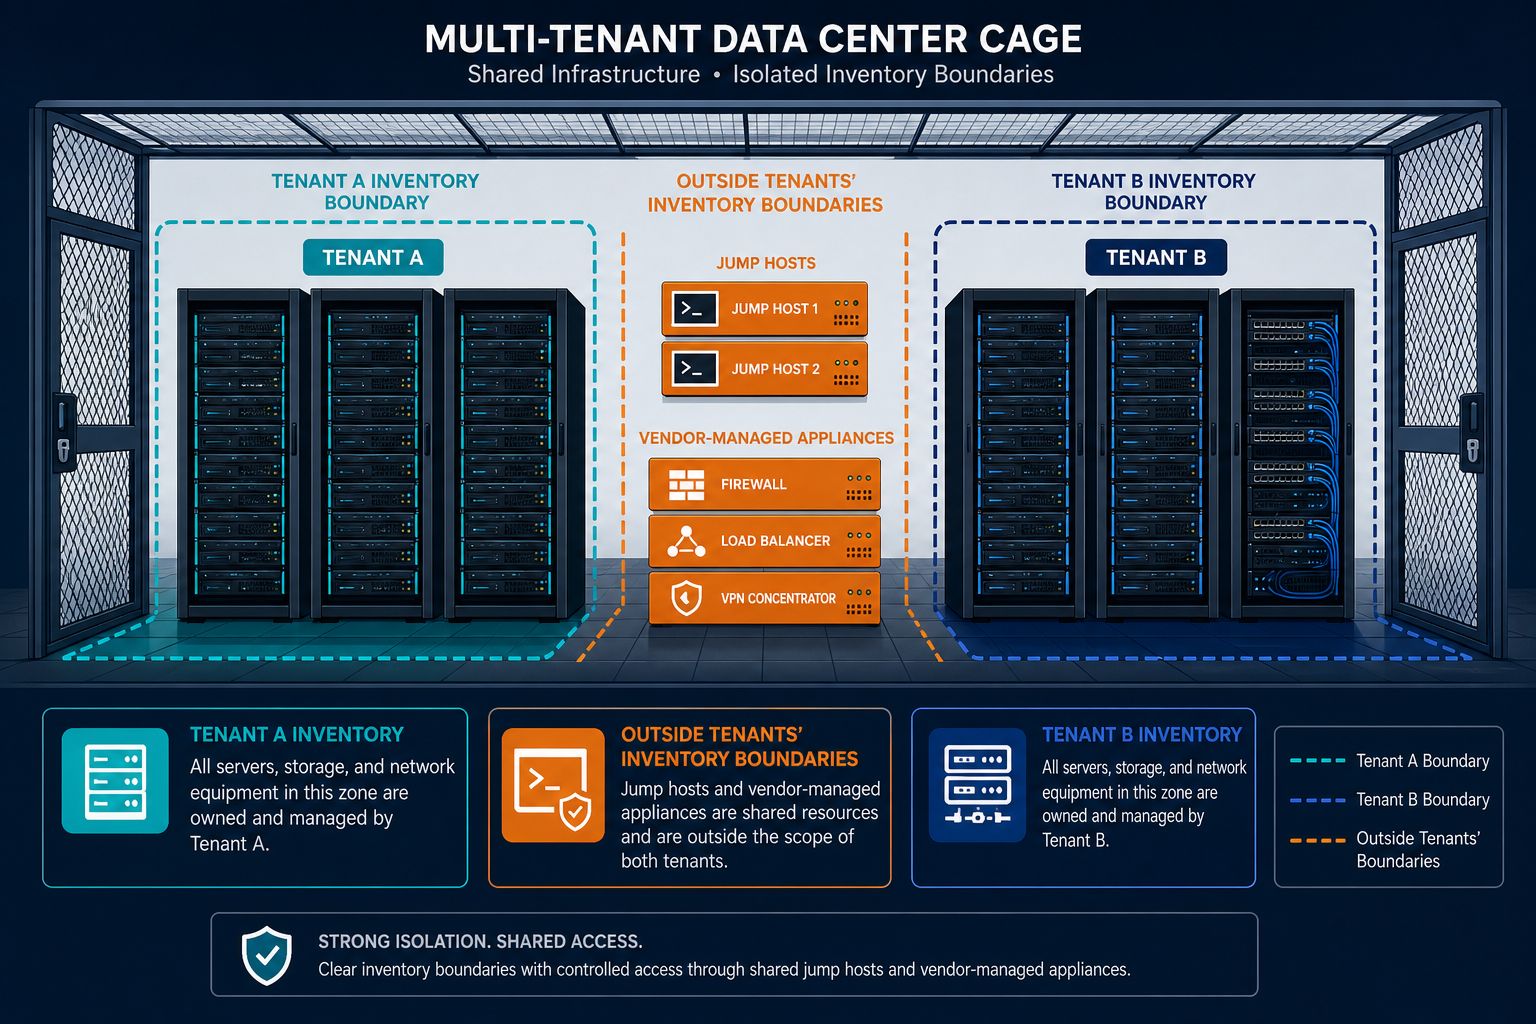
Paris manufacturers often share imaging stations, lab appliances, and vendor jump boxes with CROs and CMOs. Credential and scope limits leave dark zones. Those zones still sit inside privacy and quality risk when they carry regulated data or device-related records. For a closer look at closing those vendor-facing blind spots, see Asset Request and Form Management for Better Control and Visibility.
5. Cloud and sector SaaS without CMDB joins
Clinical, quality, and collaboration SaaS expand faster than import jobs. Subscriptions without join keys to business services break records of processing and supplier reviews. High-frequency scheduled discovery cycles plus API inventory close more of that gap than annual cloud workshops.
6. Change and decommission records that outrun last-seen
Campus moves and system retirements leave production tags on dead hosts. Continuity, privacy, and quality tests then name systems the inventory no longer supports. Stale-source quarantine is part of dual-regime readiness, not a nice-to-have cleanup. For more on keeping decommissioned hosts from lingering as phantom production assets, see blog post on stale CMDB record quarantine practices.
What inventory evidence should Paris pharma teams prepare for GDPR and EU MDR samples?
Prepare scoped personal-data systems and device quality or manufacturing paths, discovery-backed configuration items with owners and last-seen dates, service dependency joins across shared campus fabric, stale-record quarantine, and supplier touch points on production paths. Privacy and quality tests should name the same configuration items the inventory claims.
A practical dual-regime visibility packet
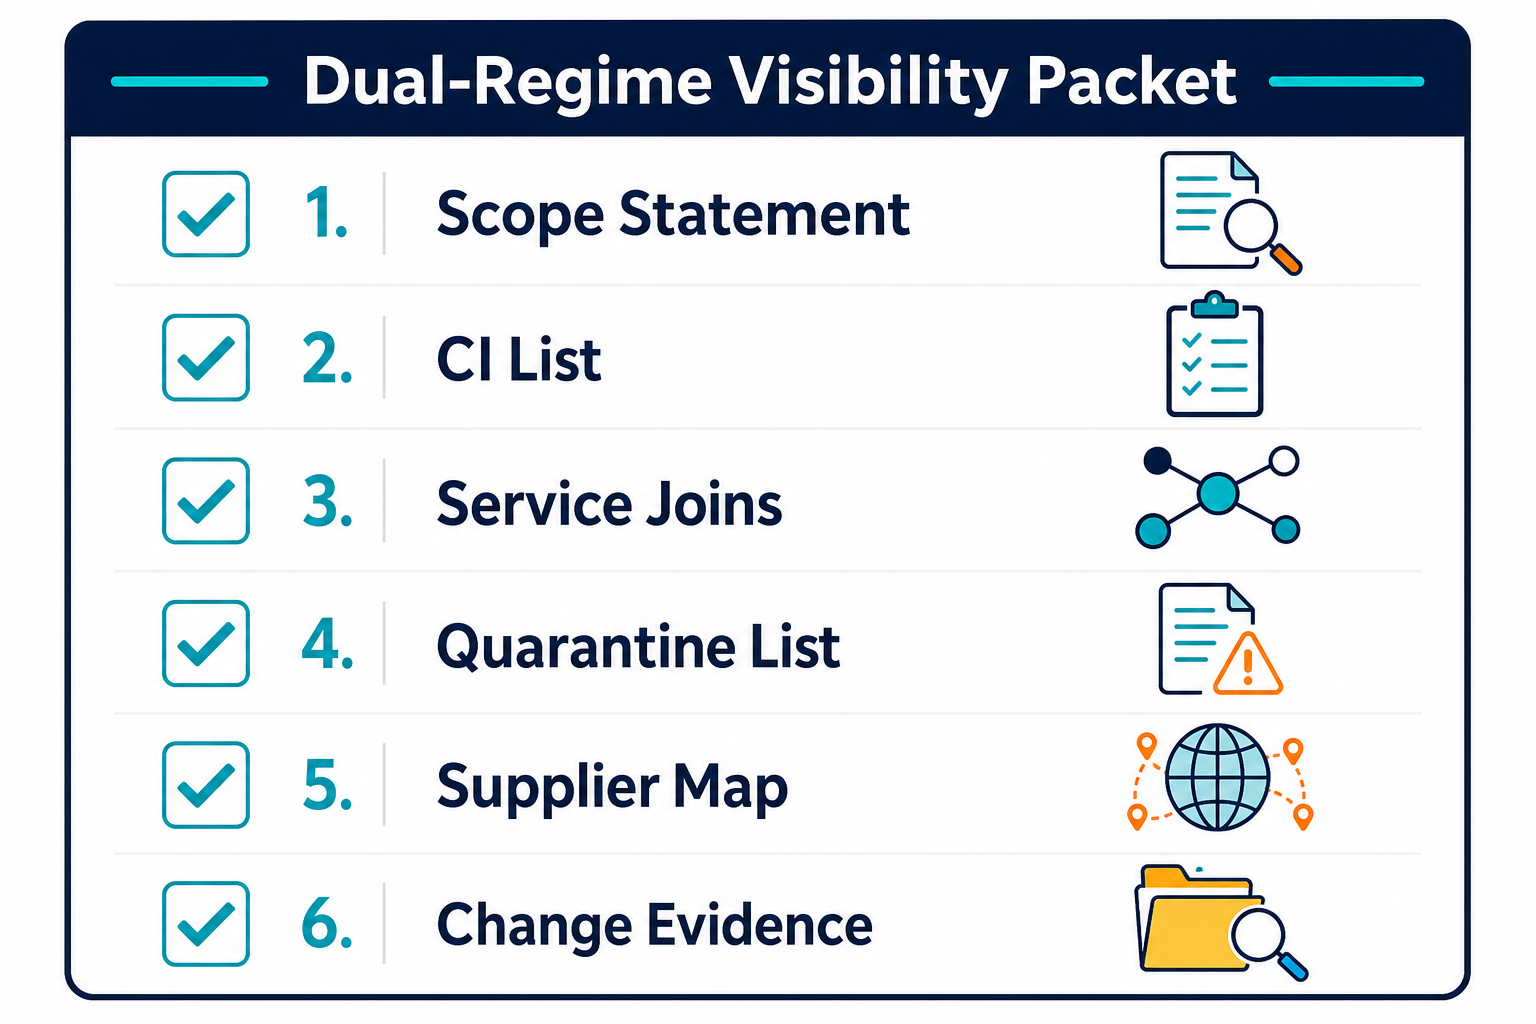
Build a packet your privacy, quality, and IT leads can defend without rewriting Union law:
- Scope statement for personal-data processing systems and device quality or manufacturing services you operate from Paris-linked estates (named paths, not vague IT).
- Discovery-backed CI list with owner, status, source, and last-seen for sampled classes (servers, network, critical endpoints, cloud accounts in scope).
- Service joins from those CIs to clinical, commercial, or device manufacturing services they support (ViVID™ maps after service definitions exist; definitions are an input, not an automatic invention).
- Stale-source quarantine list: records past freshness SLA, blocked from silent overwrite by spreadsheets.
- Supplier touch map for CROs, CMOs, and ICT suppliers that reach production or personal-data paths, scaled to actual risk.
- Change and incident evidence that names the same CIs privacy and quality samples will ask about.
Use counsel, your DPO, and quality leadership for final legal and QMS obligations. Use the Commission and EMA public pages above for orientation, then prove the system lines with live data.
Why do Paris pharmaceutical manufacturers fail dual GDPR and EU MDR inventory samples?
Personal-data hosts, validated manufacturing paths, shared lab fabric, CRO gear, and cloud control planes often sit outside a single CMDB owner model. Privacy and quality plans then reference systems whose underlying hosts have no dated discovery source. Sampling finds the gap faster than policy workshops do.
How Virima supports dual-regime visibility without replacing QMS or privacy platforms
Virima is a discovery-sourced CMDB and visibility layer. It helps Paris pharmaceutical IT teams keep estate truth current so privacy and quality programmes can cite real configuration items.
What Virima contributes
- Automated discovery across hybrid paths: Virima covers so identity keys and last-seen stay current
- CMDB records that carry source and freshness for audit sampling
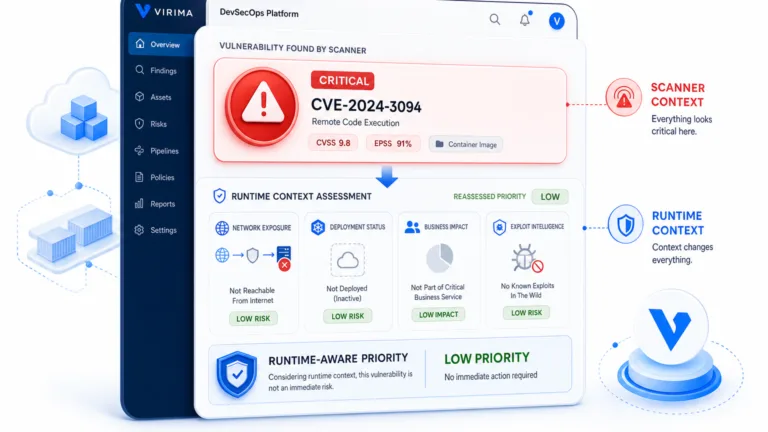
- ViVID™ service maps after service definitions are provided
- Windows Server NIST NVD overlays on maps where that signal applies, without claiming full multi-OS vulnerability management
- Publish into ServiceNow, Jira, Ivanti, and many more through one hub: all integrations
What Virima does not claim
- Autonomic Social Discovery (ASD) as a go-forward capability
- Passive continuous real-time event discovery as current product behavior
- Replacement of CNIL filings, DPO platforms, eQMS, Notified Body files, or clinical systems
- Instant invention of GxP validation status or records of processing without quality and privacy inputs
- Legal advice on GDPR or EU MDR for French manufacturers
- GCP discovery parity with AWS and Azure where product scope is cloud-limited
- OT plant control system discovery as a product claim
For capability depth, see IT discovery and CMDB.
If Paris privacy and device quality samples still name hosts your CMDB cannot own or date, walk a discovery-sourced inventory packet against the dual-regime services you must keep defensible.
Close the sample before you polish the binder
GDPR and EU MDR compliance via CMDB for Paris pharmaceutical manufacturers is won or lost on system inventory currency, dual-regime scope, owner clarity, and last-seen age, not on how thick the policy PDF is. Privacy and medical-device quality programmes still need their own controls. Those controls inherit whatever inventory quality you actually run.
When you want to pressure-test discovery coverage, and service joins on a live hybrid estate, schedule a demo.
Frequently Asked Questions
What does Virima’s CMDB show that a manual pharma asset spreadsheet doesn’t?
A manual spreadsheet records what someone typed in during the last review cycle. Virima’s discovery-sourced CMDB adds an owner, a source, and a last-seen date to each system it finds, and keeps those fields current between review cycles instead of only at audit time. That is the difference auditors test when they sample a host and ask who owns it today.
Does a CMDB replace an eQMS or Notified Body technical file under EU MDR?
No. Quality management systems and technical documentation stay in their own platforms and processes. A discovery-sourced CMDB supplies system identity, ownership, freshness, and dependency context that those quality programmes sample when they ask which IT assets support regulated paths.
How is this different from NIS2 asset visibility for La Défense finance and energy?
La Défense coverage centers on dual financial and energy essential-entity inventory under NIS2 campus density. This article centers on Paris pharmaceutical manufacturers under GDPR personal-data duties and EU MDR device quality paths, including validated and CRO-adjacent systems.
Can Virima invent GxP validation status or records of processing?
No. Validation status and records of processing stay quality and privacy inputs. Virima discovers and maps IT systems in your credentialed scope so those programmes can attach accurate hosts, owners, and last-seen dates to the systems they already govern.
What should we bring to a dual privacy and quality sample?
Bring scoped personal-data and device quality or manufacturing service lists, discovery-backed CIs with owners and last-seen, service joins across shared campus fabric, stale-record quarantine, supplier touch points you can defend, and change or incident evidence that names the same CIs. Confirm final legal and QMS obligations with counsel, your DPO, and quality leadership. That packet is what GDPR and EU MDR compliance via CMDB for Paris pharmaceutical manufacturers looks like in practice, not just in policy.