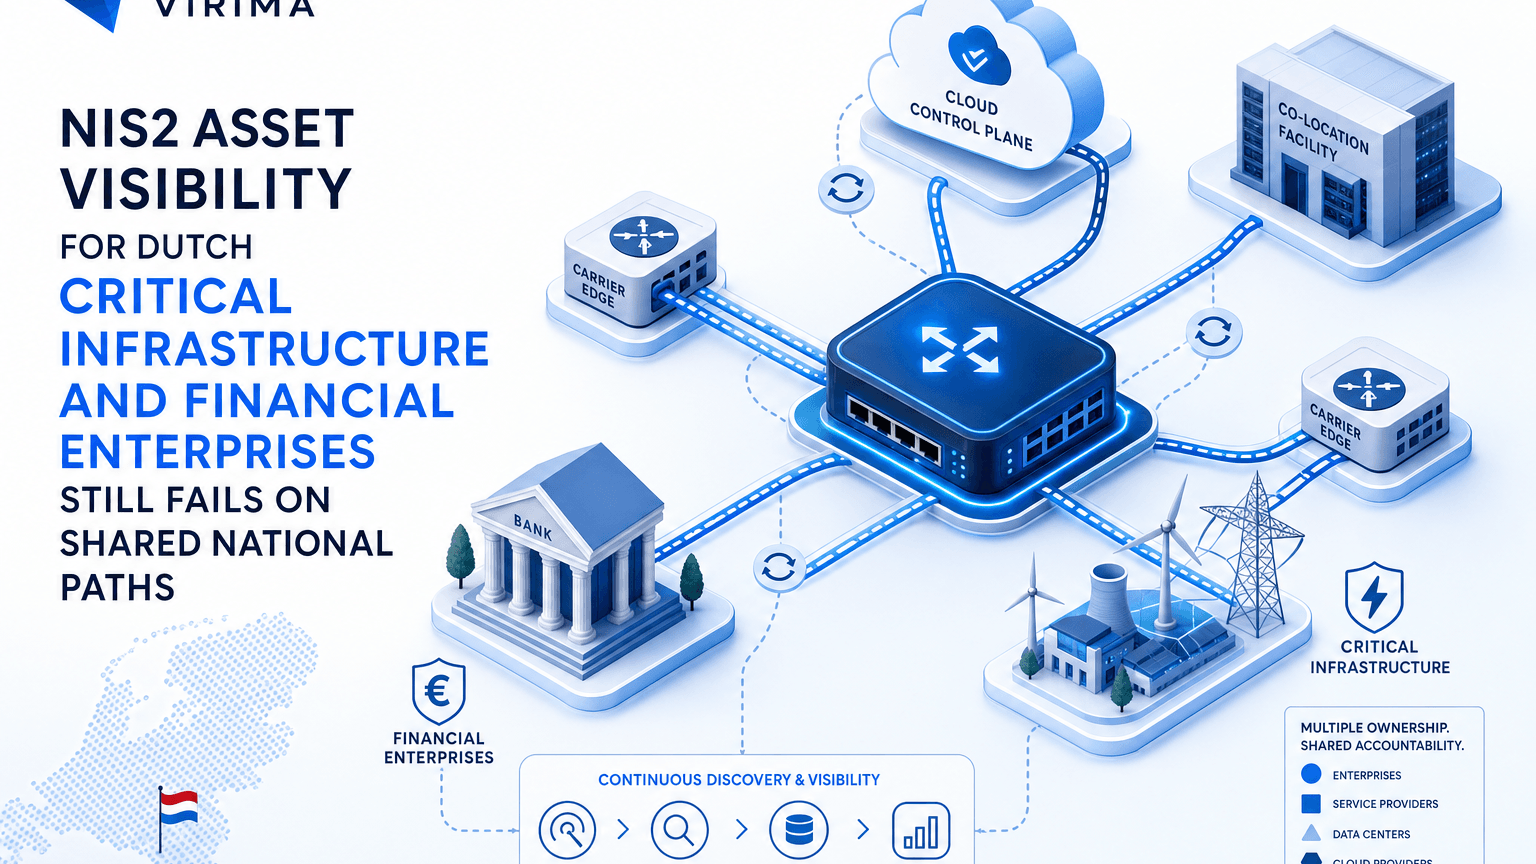
NIS2 asset visibility for Dutch critical infrastructure and financial enterprises still fails on shared national paths

Picture a competent-authority sample in the Netherlands. It doesn’t open with a policy binder. It opens with three hosts that sit under a payment path, a port or energy control path, and a shared carrier hop — then a simple ask: who owns each host today, which essential service it supports, and when that picture was last refreshed from discovery rather than a quarterly export.
That is the real test of NIS2 asset visibility for Dutch critical infrastructure and financial enterprises. Annex I and Annex II essential and important entity duties land on banks, market operators, energy, transport, digital infrastructure, and the providers that keep those services running. Spreadsheet inventories that look complete in a workshop still fail when the sample hits a shared national network path, a multi-tenant cage, a vendor jump box, or an OT-adjacent host that never sat in the CMDB.
This page is not another generic NIS2 checklist. For the cross-sector audit-day list, use NIS2 compliance checklist: what audit day actually requires. It is also not a Frankfurt FMI settlement-path piece or a La Défense dual-tower campus piece. Here the lens stays on Dutch national density: critical infrastructure operators and financial enterprises sharing fabric, contractors, and cloud control planes under Dutch and EU cyber risk measures.
For the category frame before you rewrite another inventory policy, start with Trusted Runtime Truth.
Why Dutch dual-sector estates fail inventory samples differently than a single HQ floor
The Netherlands packs ports, energy and transport corridors, financial hubs, and dense digital infrastructure into a compact national footprint. Financial entities and critical infrastructure operators often share carriers, colocation, and managed-service contractors even when they do not share risk registers. The European Commission’s NIS2 Directive page lists banking, energy, transport, and digital infrastructure among critical sectors. Visibility work fails when each sector builds its own spreadsheet and neither owns the shared hop.
| Visibility failure | What the sample often finds | Why Dutch dual-sector estates hit it first |
|---|---|---|
| Shared national fabric | Core switch or carrier edge with no single CI owner | Finance and CI tenants share the hop |
| Multi-tenant co-lo | Jump hosts and appliances outside either CMDB | Contractors refresh gear without ITAM tickets |
| OT-adjacent IT | Engineering workstations and jump boxes unscoped | CI risk measures reach IT paths finance never tracked |
| Cloud control planes | Subscriptions with no service map join | Market and CI SaaS expand faster than imports |
| Stale last-seen | Decommissioned hosts still marked production | National move projects outrun quarterly cleanups |
CISA Binding Operational Directive 23-01 is a U.S. federal inventory rule, not EU law. Enterprise programs still use the same operational lesson: incomplete asset inventories break every control that claims coverage. Dutch cyber context still sits under the NCSC, while prudential and cyber-risk supervision of financial entities sits under De Nederlandsche Bank (DNB) — a distinct role from the AFM’s market-conduct remit. Neither path excuses undated inventory.
What NIS2 asset visibility means for Dutch operators
NIS2 asset visibility for Dutch critical infrastructure and financial enterprises means a dated, owned overview of the IT assets and dependencies that support essential financial and critical-infrastructure services in scope for your entity type, refreshed from discovery-sourced records rather than one-off workshops.
It is not:
- A substitute for Dutch transposition advice or NCSC engagement
- A full Digital Operational Resilience Act (DORA) ICT-risk programme by itself for financial entities
- A claim that Virima is a GRC, CSIRT portal, OT historian, or regulatory filing tool
It is the infrastructure evidence layer that risk analysis, incident handling, supply chain security, and continuity testing all lean on. ENISA’s NIS2 Technical Implementation Guidance turns Article 21-style measures into technical expectations. None of that guidance treats an undated spreadsheet as proof that asset security holds under sampling.
National transposition of NIS2 into Dutch law, the Cyberbeveiligingswet, has continued to move through the legislative process, and Commission-level enforcement activity against Member States over incomplete transposition has continued alongside it. Operators still face national competent authorities and CSIRT reporting clocks. Inventory currency does not wait for a transposition timeline to finish.
What is NIS2 asset visibility for Dutch critical infrastructure and financial enterprises?
It is a discovery-sourced, owned inventory of systems and dependencies that support essential financial and critical-infrastructure services in scope on dense Dutch national estates. Auditors sample hosts, owners, freshness dates, and service joins. Policy binders without that evidence fail the same controls they claim to meet.
Five inventory gaps that break Dutch dual-sector samples
1. Shared national fabric without a single accountable owner
A core switch or carrier edge can sit under both a payment path and a port or energy path and still have three owners in three tools. NIS2 accountability and access-control measures need one accountable role per relevant asset. Discovery that only populates hardware without owner fields leaves the governance gap open.
2. Multi-tenant co-location treated as someone else’s problem
Dutch estates often mix owned floors, shared cages, and vendor-managed appliances. Credential and scope limits leave dark zones. Those zones still sit inside essential-entity risk measures when they carry market or critical-infrastructure traffic.
3. OT-adjacent IT left outside the financial CMDB
Critical infrastructure operators bring engineering workstations, jump boxes, and plant-facing interfaces into the same national network story as finance IT. Dual-sector holding groups that invent one inventory for banking and another for infrastructure miss the shared IT layer both risk programmes inherit.
4. Cloud control planes and sector SaaS without CMDB joins
Surveillance, market data, energy trading, transport systems, and collaboration SaaS expand faster than import jobs. Subscriptions without join keys to business services break supply chain and access reviews. High-frequency scheduled discovery cycles plus API inventory close more of that gap than annual cloud workshops.
5. Partner and upstream dependencies with no last-verified edge
Continuity depends on other entities. You cannot discover every partner’s private estate. You can still record the interfaces, circuits, and systems you own that connect to them, with last-verified dates. That is the evidence supply chain security reviews actually sample.
What inventory evidence should Dutch teams prepare for NIS2 sampling?
Prepare scoped essential services for finance and critical infrastructure where both apply, discovery-backed configuration items with owners and last-seen dates, service dependency joins across shared national paths, stale-record quarantine, and supplier touch points on production paths. Continuity and incident tests should name the same configuration items the inventory claims.
A practical visibility packet before the next competent-authority conversation
Build a packet your risk, IT, and compliance leads can defend without rewriting NIS2 law:
- Scope statement for essential services you operate from Dutch-linked estates (named finance and critical-infrastructure services, not vague IT).
- Discovery-backed CI list with owner, status, source, and last-seen for sampled classes (servers, network, critical endpoints, cloud accounts in scope).
- Service joins from those CIs to the market, payment, energy, transport, or digital services they support (ViVID™ maps after service definitions exist; definitions are an input, not an automatic invention).
- Stale-source quarantine list: records past freshness SLA, blocked from silent overwrite by spreadsheets.
- Supplier touch map for direct ICT suppliers that reach production paths, scaled to actual risk.
- Incident and continuity test evidence that names the same CIs the inventory claims.
Use national transposition and legal counsel for final obligations. Use nis2directive.eu requirements as a plain-language orientation to the four pillars and minimum measures, then prove the asset lines with live data.
Why do Dutch critical infrastructure and financial teams fail NIS2 inventory samples?
Shared national fabric, multi-tenant co-location, OT-adjacent IT, and cloud control planes often sit outside a single CMDB owner model. Continuity and incident plans then reference services whose underlying hosts have no dated discovery source. Sampling finds the gap faster than policy workshops do.
How Virima supports NIS2 asset visibility without replacing your GRC stack
Virima is a discovery-sourced CMDB and visibility layer. It helps financial and critical-infrastructure IT teams in the Netherlands keep estate truth current so risk, incident, and continuity programmes can cite real configuration items.
What Virima contributes
- Automated discovery across hybrid paths Virima covers so identity keys and last-seen stay current
- CMDB records that carry source and freshness for audit sampling
- ViVID™ service maps after service definitions are provided
- Windows Server NIST NVD overlays on maps where that signal applies, without claiming full multi-OS vulnerability management
- Publish into ServiceNow, Jira, Ivanti, and many more through one hub: all integrations
What Virima does not claim
- Autonomic Social Discovery (ASD) as a go-forward capability
- Passive continuous real-time event discovery as current product behavior
- Replacement of NCSC filings, CSIRT portals, GRC platforms, or OT control systems
- Instant invention of business services without a definition input
- Full DORA ICT-risk management or third-party register product coverage
- GCP discovery parity with AWS and Azure where product scope is cloud-limited
- Legal advice on Dutch NIS2 transposition
For capability depth, see IT discovery and CMDB.
If Dutch finance and critical-infrastructure paths still sit on hosts your CMDB cannot own or date, walk a discovery-sourced inventory packet against the shared national services you must keep available under NIS2.
Close the sample before you polish the binder
NIS2 asset visibility for Dutch critical infrastructure and financial enterprises is won or lost on shared national paths, dual-sector scope, owner currency, and last-seen age, not on how thick the policy PDF is. Essential-entity duties still need risk measures, incident handling, supply chain security, and continuity plans. Those controls inherit whatever inventory quality you actually run.
When you want to pressure-test discovery coverage and service joins on a live hybrid estate, schedule a demo.
Frequently Asked Questions
Is this the same as a full NIS2 compliance checklist?
No. A full checklist covers risk measures, accountability, reporting, and continuity across sectors. This article focuses on IT asset and dependency visibility for Dutch critical infrastructure and financial estates that often fail the inventory sample first on shared national paths.
How is this different from NIS2 visibility for Frankfurt financial market infrastructure?
Frankfurt coverage centers on settlement and market-path hosts for FMI operators. See Asset Request and Form Management for Better Control and Visibility. Dutch coverage centers on dual-sector national density where critical infrastructure and financial enterprises share carriers, fabric, and contractors under one compact footprint.
How is this different from NIS2 visibility for La Défense finance and energy?
La Défense coverage centers on dual financial and energy tower campus density in the Paris business district. See Asset Request and Form Management for Better Control and Visibility. Dutch coverage centers on national critical infrastructure plus financial enterprises sharing national paths, ports, energy corridors, and digital infrastructure, not only a single business-district campus.
Does NIS2 asset visibility replace DORA work for financial entities?
No. DORA is a separate EU digital operational resilience framework for the financial sector. Inventory and dependency truth still feed both programmes. Treat them as related evidence needs, not as one product checkbox.
Can Virima discover OT plant systems for critical infrastructure operators?
Virima discovers and maps IT systems in your credentialed scope. OT plant systems and industrial control planes stay outside that claim. Record OT-adjacent IT interfaces you own, with last-verified dates, for the inventory evidence risk programmes sample.