Hybrid Cloud Architecture: Examples, Diagram & Use Cases

Hybrid cloud architecture is an IT infrastructure model. It connects on-premises data centers, private clouds, and public cloud platforms (such as AWS and Azure) under a single management layer. According to Gartner’s November 2024 forecast, 90% of organizations will adopt hybrid cloud through 2027.
The operational challenge after deployment is keeping track of what runs where. According to the Flexera 2026 State of the Cloud Report, 73% of organizations now combine public and private cloud environments in a hybrid model. As assets span AWS, Azure, and on-premises racks at the same time, your CMDB must reflect all three tiers accurately. Otherwise, it develops gaps that affect every downstream process. This guide covers the architecture, common use cases, deployment patterns, and the CMDB requirements of a distributed IT estate.
What Is Hybrid Cloud Architecture?
Private infrastructure covers on-premises data centers and private clouds, while public cloud services such as AWS and Azure provide elastic compute, storage, and managed services. Regulated data stays on private infrastructure, and elastic workloads scale in the public cloud. A workload can run on a single tier, move between tiers, or span tiers, depending on demand, cost, and compliance requirements.
The three foundational components of a hybrid cloud deployment are:
- Private infrastructure: on-premises servers, data centers, or hosted private cloud environments that the organization controls exclusively.
- Public cloud services: Infrastructure-as-a-Service (IaaS), Platform-as-a-Service (PaaS), and SaaS resources from providers such as AWS or Azure.
- Connectivity layer: VPN tunnels, dedicated connections (AWS Direct Connect, Azure ExpressRoute), or software-defined networking that enables secure communication between environments.
Modern hybrid cloud architecture often adds container orchestration platforms like Kubernetes. These platforms let teams deploy workloads consistently across on-premises and cloud environments. Teams can do this without rewriting applications for each target.
| What is hybrid cloud architecture? Hybrid cloud architecture is an IT infrastructure model that connects on-premises data centers, private clouds, and public cloud platforms such as AWS and Azure into a single managed environment. Organizations use it to run workloads where they make operational, financial, and compliance sense, with secure connectivity binding all three tiers together. |
Benefits of Hybrid Cloud Architecture
Hybrid cloud architecture gives IT teams a framework for managing competing priorities. Specifically, it addresses challenges that no single-tier deployment can resolve. Four operational benefits account for most enterprise adoption:
- Workload flexibility: teams place compute where it makes the most financial sense. High-cost workloads run on elastic public cloud capacity, while latency-sensitive or compliance-bound workloads stay on private infrastructure.
- Compliance coexistence: regulated data stays on private infrastructure where sovereignty and residency requirements apply. Analytics and development workloads, in contrast, run on public cloud without creating a compliance exposure.
- Elastic capacity: private infrastructure handles steady-state load. Public cloud absorbs demand spikes without requiring permanent capital investment in on-premises hardware.
- Incremental migration: organizations move workloads gradually rather than committing to a full-stack migration before legacy systems are ready. The hybrid state is a deliberate operational model, not a transitional failure mode.
Together, these four benefits explain why hybrid cloud is a deliberate long-term operating model for most enterprises. It is not merely a transitional state.
| What are the benefits of hybrid cloud architecture? Hybrid cloud architecture delivers four operational benefits: workload flexibility to place compute where it is most cost-effective, compliance alignment to keep regulated data on private infrastructure, elastic capacity to absorb demand spikes without permanent capital investment, and incremental migration paths that let teams move workloads gradually without decommissioning on-premises systems before cloud readiness is established. |
How a Hybrid Cloud Architecture Diagram Is Structured
A hybrid cloud architecture diagram maps the three infrastructure tiers and the data flows connecting them. A standard diagram includes five key elements:
- On-premises layer: physical servers, local storage systems, and legacy applications.
- Private cloud layer: virtualized infrastructure with isolated compute and storage, hosted on-premises or in a colocation facility.
- Public cloud layer: elastic compute, cloud-native databases, and SaaS integrations running in AWS or Azure.
- Connectivity: the network paths (VPN tunnels, dedicated links, service meshes) that bind all three tiers.
- Management plane: the unified control layer where teams provision, monitor, and govern workloads across all environments.
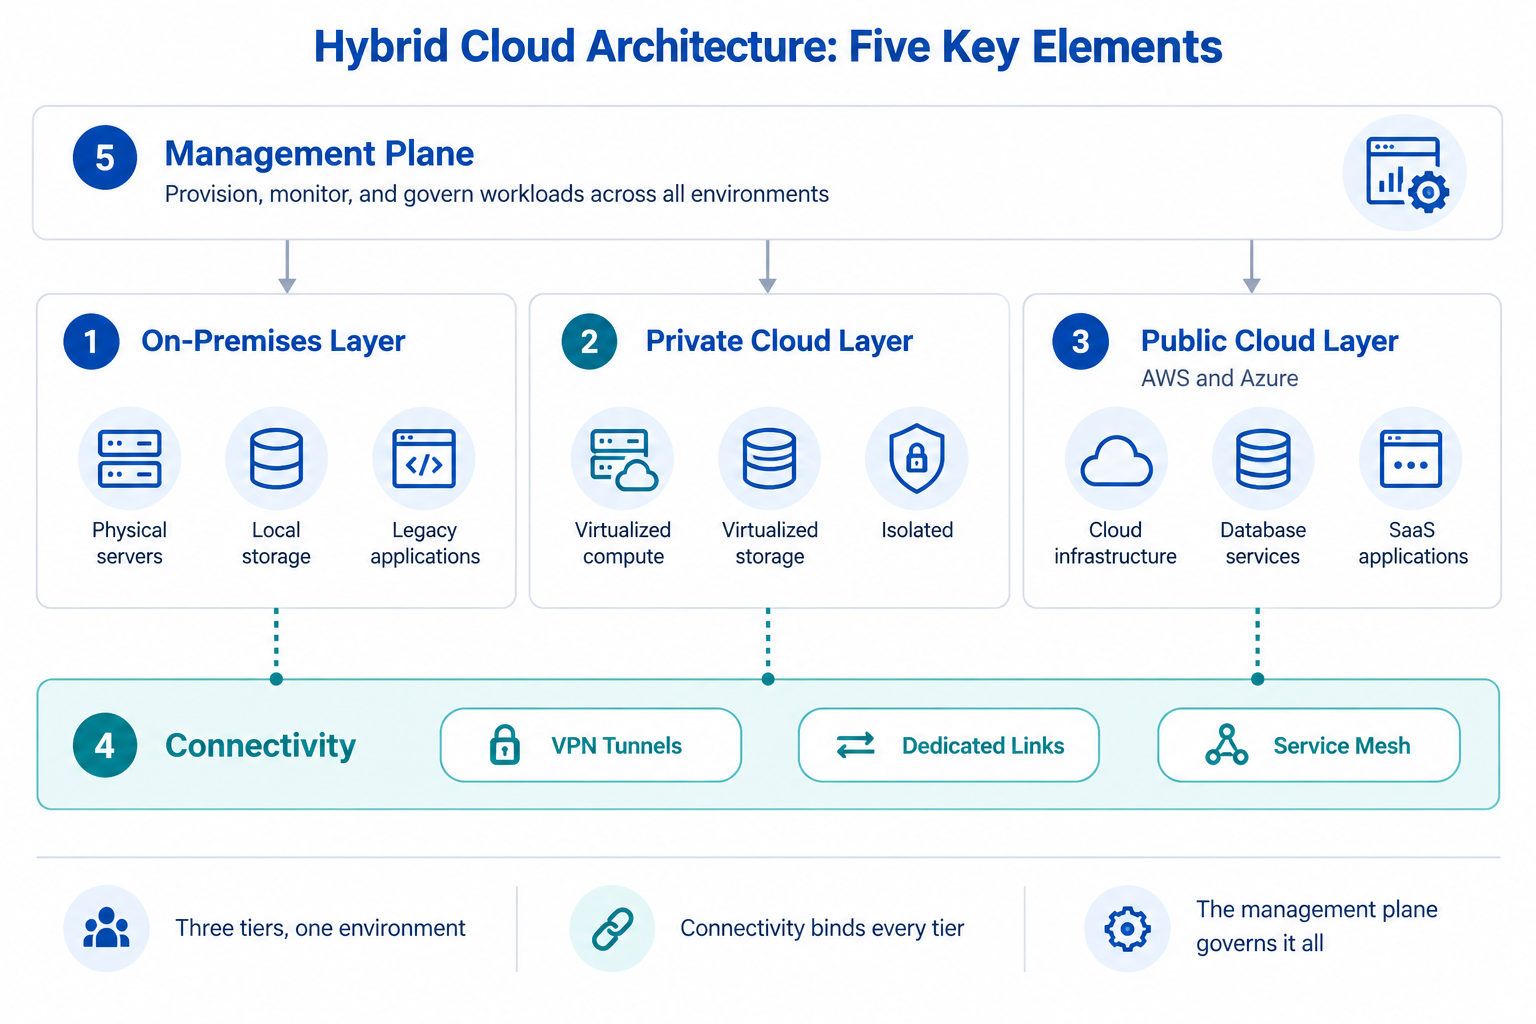
The management plane is where most teams underinvest. Connectivity and provisioning tooling are relatively mature. However, maintaining an accurate, regularly refreshed inventory across all three tiers is far more difficult. That inventory must include ownership, configuration state, and service dependencies. Without it, hybrid cloud environments develop blind spots that compound over time.
Those gaps make change management and incident response progressively harder. Consequently, the management plane deserves as much investment as the connectivity layer.
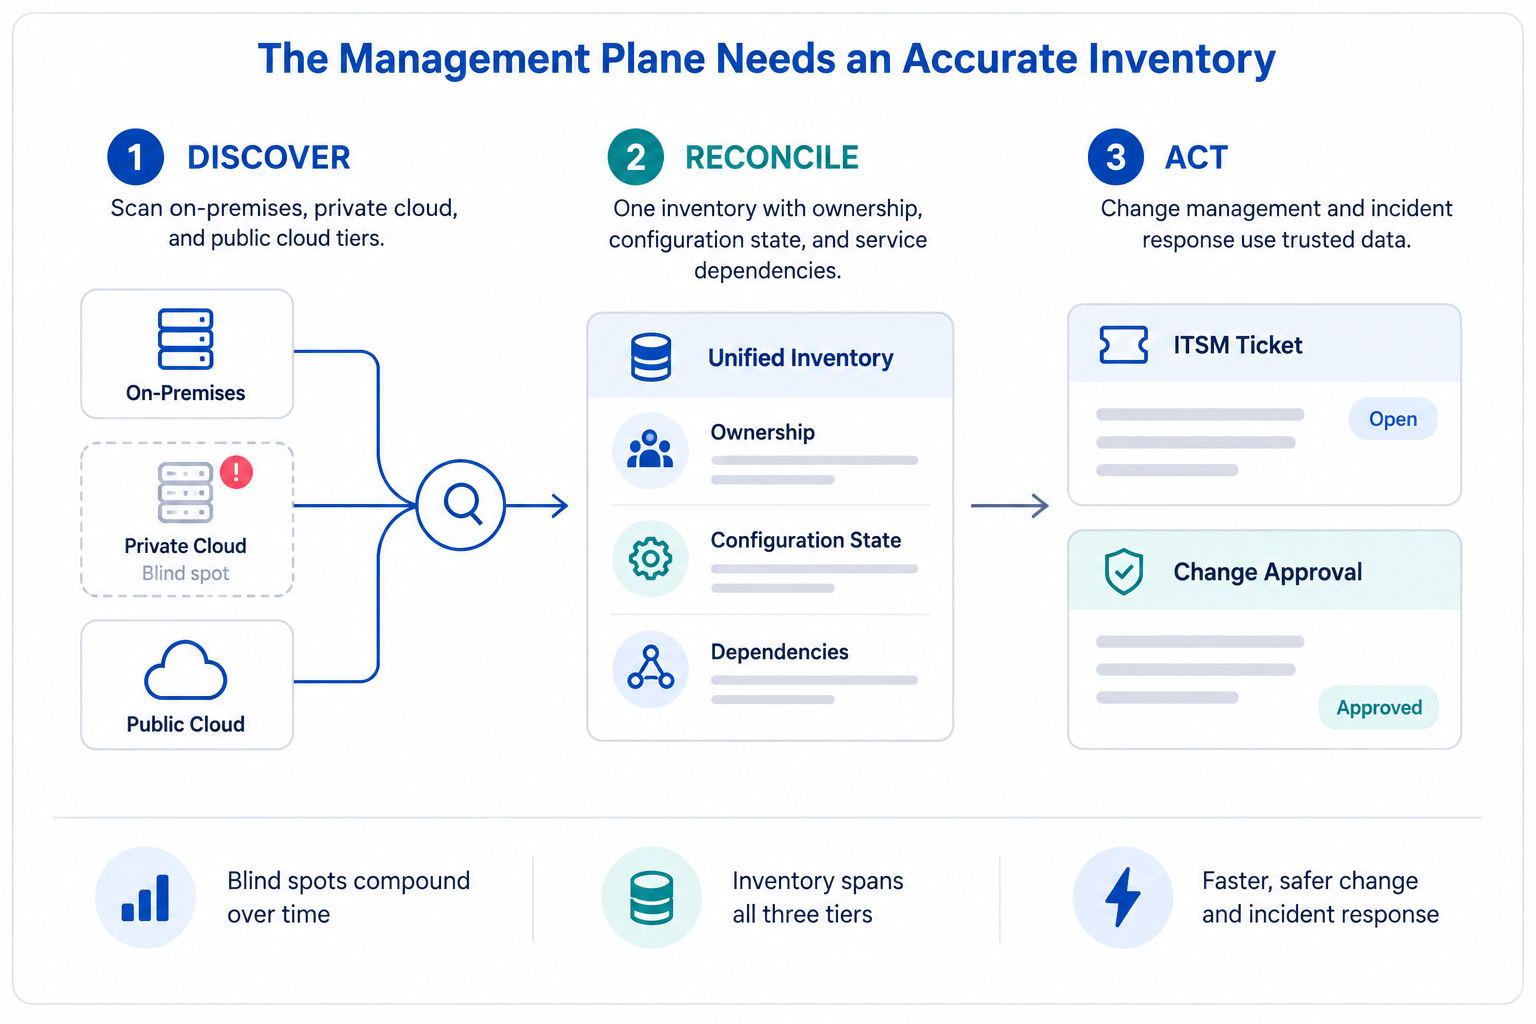
| What does a hybrid cloud architecture diagram show? A hybrid cloud architecture diagram shows three infrastructure tiers (on-premises, private cloud, and public cloud) connected by network paths such as VPN tunnels or dedicated links like AWS Direct Connect. A complete diagram also includes the management plane that governs workloads |
Common Hybrid Cloud Use Cases
Hybrid cloud architecture deployments appear across industries for different operational reasons. Seven patterns account for most enterprise implementations.
Regulatory Data Residency
Financial services and healthcare organizations keep sensitive data on private infrastructure. This approach helps them meet HIPAA, PCI-DSS, and SOX requirements. As a result, analytics and non-regulated workloads run on public cloud, where compute costs are lower. The architecture lets compliance and cost optimization coexist without conflict.
Cloud Bursting
Applications run on private infrastructure at normal load. During demand spikes, such as seasonal traffic peaks or batch processing cycles, workloads extend into public cloud capacity. They then contract when demand subsides. The private tier handles baseline load; the public tier absorbs the peak.
Disaster Recovery and Business Continuity
On-premises primary systems replicate to cloud-based secondary environments. When primary infrastructure fails, workloads fail over to the cloud. However, this requires accurate IT asset management records as a prerequisite. You cannot recover what you have not documented.
Phased Migration
Organizations rarely move from on-premises to cloud in a single event. Instead, a phased hybrid cloud migration strategy lets teams move workloads incrementally. Teams validate performance and dependencies before decommissioning on-premises resources. The hybrid state is intentional and may last years.
Legacy Application Integration
Some applications cannot be refactored for the cloud. They stay on-premises, while new cloud-native services consume their data via APIs. This approach lets organizations preserve legacy systems while building new capabilities on top of them.
Edge Computing
Certain workloads require low-latency processing, such as IoT data collection, branch office operations, or remote analytics. In these cases, edge nodes process data locally while syncing results back to central cloud or on-premises infrastructure. Edge computing, therefore, extends the hybrid cloud model beyond the data center. It adds a fourth tier that demands its own discovery and asset tracking.
Application Modernization
Application modernization is a common use case for enterprises with large portfolios of on-premises software. Teams decompose legacy monoliths into microservices incrementally. New components deploy to cloud environments, while the existing on-premises application continues operating. As a result, the hybrid state enables continuous delivery of modernized capabilities without a disruptive full-stack migration.
Hybrid Cloud Storage Architecture
A specific subset of hybrid use cases is storage tiering. Frequently accessed data stays on-premises or in a private cloud for latency and performance. Cold data and backups, in contrast, move to cloud object storage, where per-GB costs are significantly lower. A tiering policy governs which data lives where and when it migrates between tiers.
Hybrid cloud storage architecture requires discovery-driven asset management. Specifically, teams need to track what data lives where, who owns it, and when it was last accessed.
| What are common hybrid cloud use cases? Common hybrid cloud use cases include regulatory data residency, cloud bursting to handle demand spikes, disaster recovery from on-premises to cloud, phased migration strategies, legacy application integration, edge computing, and application modernization. Most enterprise implementations combine several of these patterns at the same time. |
Hybrid Cloud Deployment Patterns
Three primary patterns describe how organizations move workloads into a hybrid cloud architecture. Each creates different demands on agent-based or agentless discovery and CMDB accuracy. Understanding which pattern matches your workload type is one of the first decisions IT teams make when planning a hybrid cloud migration.
Lift and Shift
This is the fastest path. Existing applications move to the public cloud with minimal changes. Infrastructure requirements change; the application logic does not. Lift-and-shift is a common starting point for hybrid cloud migration. However, it rarely captures the full cost benefits of cloud-native design.
Refactor
Specific application components get rewritten as microservices and deployed in containers. This makes workloads portable across all three tiers. Most enterprise hybrid cloud environments evolve toward this model. Containerized workloads run on any tier without environment-specific configuration.
Cloud-Native Build
New applications are designed from the start for hybrid deployment. They use container orchestration, infrastructure-as-code, and API-based service composition. As a result, these workloads move freely across tiers without operational friction.
Each pattern places different demands on IT discovery. Lift-and-shift changes where a workload runs. Refactoring, in contrast, changes how it is structured. Cloud-native builds introduce configuration items with no on-premises equivalent. In all three cases, the CMDB needs to know about the change. Manual update processes rarely keep pace.
| Hybrid cloud architecture introduces four main challenges: asset visibility across multiple environments, network complexity between tiers, inconsistent identity and access management, and compliance gaps when data moves across environments. Each challenge compounds when organizations lack a unified CMDB built from live discovery data across all three tiers. |
Challenges of Hybrid Cloud Architecture
Hybrid cloud architecture introduces operational challenges that single-environment deployments avoid. Below are the four most common ones IT teams encounter.
Asset Visibility and Sprawl
Assets exist across multiple environments with different inventory formats, naming conventions, and ownership structures. Without CMDB discovery that bridges on-premises and cloud, records from each tier are rarely reconciled. Drift between tiers affects incident response and change management decisions.
IT teams end up maintaining separate inventories that disagree with each other.
Network Complexity
Latency between tiers, inconsistent routing, and misconfigured VPN tunnels are among the most common causes of application performance issues in hybrid cloud architecture. According to the Uptime Institute 2025 Annual Outage Analysis, 54% of respondents to its 2024 survey said their most recent significant outage cost more than $100,000.
Understanding failure impact when a network component fails requires accurate dependency mapping across all three tiers. That, in turn, starts with understanding hybrid and multi-cloud network topologies.
Identity and Access Management Inconsistency
Each environment carries its own IAM model: on-premises Active Directory, AWS IAM, and Azure Entra. Reconciling identities across all three requires deliberate policy design and regular auditing. Service accounts and machine identities that span environments carry the highest risk. They are invisible to any single environment’s native security tooling.
Without a unified identity audit across all three tiers, cross-environment access gaps go undetected. They typically surface only during a compliance review or after an incident.
| How do you secure identity and access management across a hybrid cloud architecture? Securing hybrid cloud architecture requires reconciling three identity systems simultaneously: on-premises Active Directory, AWS IAM, and Azure Entra ID. Service accounts and machine identities that span all three environments are the highest-risk surface. They are invisible to any single environment’s native security tooling. A unified identity audit across all three tiers is required to detect and close cross-environment access gaps before they surface in a compliance review or incident. |
Governance and Compliance Gaps
When data moves between environments, compliance obligations follow the data. However, that only holds if the organization can trace where assets reside and who owns them. Organizations without that traceability face audit exposure.
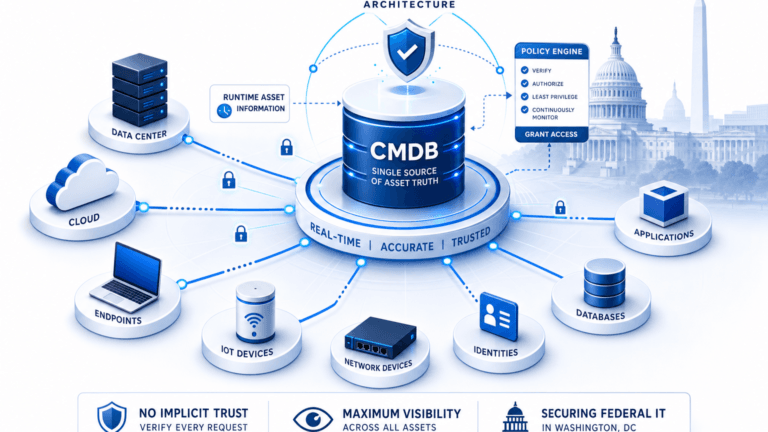
To build a CMDB that accurately reflects a hybrid cloud architecture, discovery must reach every tier. The original CMDB design rarely covers all three layers.
| What are the main challenges of hybrid cloud architecture? The primary challenges of hybrid cloud architecture are asset visibility across multiple environments, network complexity between tiers, inconsistent identity and access management, and compliance gaps when data moves between private and public cloud. Each challenge grows more difficult when organizations lack a unified CMDB built from live discovery data across all three tiers. |
How CMDB Accuracy Works Across a Hybrid Cloud Architecture
A hybrid cloud architecture creates two connected discovery problems. The first is breadth: assets exist on AWS, Azure, and on-premises at the same time. The second is rate of change: cloud assets are created, modified, and decommissioned at a pace that manual CMDB update processes cannot match.
Discovery Breadth Across Three Tiers
Virima addresses both discovery problems using a parallel approach. Specifically, Virima combines agent-based and agentless discovery with API-based scanning for AWS and Azure. Configuration items are built from live discovery data across all three tiers. Asset records, relationships, ownership, and configuration state are regularly refreshed from actual discovery results.
Passive discovery approaches can miss short-lived cloud instances created and terminated between scan windows. Virima, therefore, uses high-frequency discovery cycles to reduce that gap across both cloud and on-premises tiers.
Service-Layer Visibility with ViVID™
ViVID™ service maps extend this visibility to the service layer. Once discovery data populates the CMDB, ViVID™ builds dependency maps showing which applications, services, and infrastructure components connect to each other across all three tiers. When something fails in the hybrid environment, the blast radius is visible before an incident becomes an outage.
| See how Virima maintains discovery-driven accuracy across hybrid cloud environments, including AWS and Azure asset discovery, at Virima Trusted Runtime Truth. |
ITSM Integration for Hybrid Cloud Teams
For teams using ServiceNow or Jira Service Management as their ITSM platform, Virima syncs CI data bidirectionally. Incident responders and change approvers, therefore, see accurate, up-to-date asset data in the tools they already use. There is no need for a separate lookup.
This integration ensures that hybrid cloud asset changes appear in ITSM workflows automatically. As a result, the risk of decisions based on stale data is significantly reduced.
| How do you maintain CMDB accuracy in a hybrid cloud environment? Maintaining CMDB accuracy across a hybrid cloud architecture requires three discovery methods operating in parallel: API-based discovery for AWS and Azure cloud accounts, agent-based discovery for on-premises servers and endpoints, and agentless scanning for network devices and systems where agents cannot be deployed. Without all three methods covering all three tiers simultaneously, cloud-native and on-premises assets appear in separate, unreconciled inventories that degrade incident and change management. |
Hybrid Cloud Managed Services and Governance
Hybrid cloud managed services are third-party providers or platform-native tooling that handle day-two operations across hybrid environments. These services typically cover monitoring, patching, capacity management, and compliance reporting. Organizations use them when internal teams cannot staff operations across all three tiers simultaneously.
Regardless of whether operations are managed internally or externally, governance depends on the same foundation. That foundation is an accurate inventory of every asset, its configuration state, and its relationships to other assets and services. Providers working from stale CMDB data, therefore, carry the same blind spots as the internal teams they replace.
Hybrid cloud architecture distributes operational risk across tiers. Without discovery-driven CMDB accuracy spanning all three environments, that distribution creates more surface area for failure. Effective governance, consequently, starts with discovery.
| Schedule a demo to learn how Virima connects discovery-driven CMDB data with your ITSM platform. |
Frequently Asked Questions
What is the difference between hybrid cloud and multi-cloud architecture?
Hybrid cloud architecture connects on-premises or private infrastructure with one or more public cloud platforms. Multi-cloud refers specifically to using multiple public cloud providers together (such as AWS and Azure) without necessarily including on-premises infrastructure. The two frequently overlap. Many organizations, in fact, run hybrid multi-cloud environments that combine private infrastructure with two or more public cloud providers.
What are the most common examples of hybrid cloud architecture?
Common hybrid cloud examples include financial organizations keeping regulated data on-premises while running analytics workloads in AWS, healthcare providers using private cloud for patient records and public cloud for development environments, and enterprises extending on-premises applications into public cloud during peak load via cloud bursting. Phased migration, where teams move workloads incrementally while maintaining a hybrid state for months or years, is among the most widely deployed patterns.
What is the difference between hybrid cloud and private cloud?
A private cloud is infrastructure a single organization controls exclusively, hosted on-premises or in a colocation facility, with no public cloud component. Hybrid cloud architecture, in contrast, connects that private infrastructure to one or more public cloud platforms via secure networking. This enables workload portability between environments. Private cloud is isolation; hybrid cloud is integration across controlled and shared infrastructure simultaneously.
Does Virima discover assets across hybrid cloud environments?
Yes. Virima uses three parallel discovery methods: API-based scanning for AWS and Azure cloud accounts, agent-based discovery for on-premises servers and endpoints, and agentless scanning for network devices where agents cannot be deployed. All three feed into a shared CMDB. Cloud and on-premises assets are, therefore, tracked in a single inventory with regular refresh cycles.
Does Virima integrate with ServiceNow or Jira Service Management for hybrid cloud visibility?
Yes. Virima syncs configuration item data bidirectionally with ServiceNow and Jira Service Management. Incident responders and change approvers, therefore, see accurate, discovery-sourced asset data in the ITSM tools they already use. Other supported ITSM platforms include Ivanti, HaloITSM, Hornbill, and Xurrent. For hybrid cloud environments, this means ITSM tickets automatically reflect which cloud or on-premises assets are involved, without a separate CMDB lookup.